Security operations
Investigating endpoint alerts, phishing campaigns, malicious URLs, and suspicious activity with a focus on clear triage.
AUNG B. MHN / CYBERSECURITY
SECURITY OPERATIONS & GRC
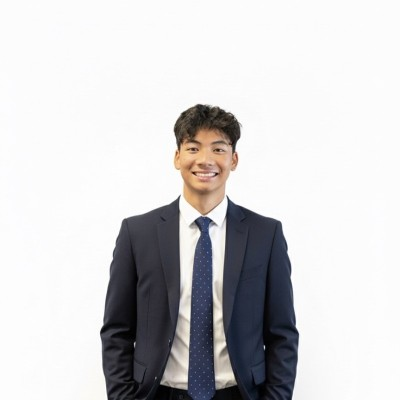
I’m a Computer Engineering Technology graduate from Purdue University pursuing opportunities in Security Operations (SOC) and Governance, Risk & Compliance (GRC). I enjoy hands-on investigation, automation, and translating technical findings into clear risk decisions.
Explore my work01 / THE PERSON BEHIND THE PROCESS
My background brings together computer engineering, banking, team leadership, and hands-on security operations.
I earned my B.S. in Computer Engineering Technology at Purdue University, with a minor in Information Technology. Today, I investigate endpoint and email threats at STAR Financial Bank, working with Microsoft Defender and Rapid7 InsightIDR.
My banking experience taught me to pay attention to details, document clearly, and handle exceptions with care. I bring that same approach to security: understand the evidence, make the next step clear, and build processes others can rely on.
Outside of work, I enjoy rock climbing, snowboarding, and skydiving. Each challenges me to assess risk, prepare carefully, and stay focused when conditions change. Rock climbing especially pushes me to think through a problem, try an approach, and adapt.
That same curiosity draws me to cybersecurity. I enjoy figuring out what happened, spotting patterns, and finding ways to protect people and systems. Whether I’m investigating a suspicious email or working through a climbing route, I like turning an unfamiliar challenge into something I can understand.
enterprise assets supported through
inventory reconciliation and automation
02 / WHAT I BRING
Tools matter. Knowing how to connect
the evidence is what makes them useful.
Investigating endpoint alerts, phishing campaigns, malicious URLs, and suspicious activity with a focus on clear triage.
Searching logs, examining network traffic, and developing detections that surface potential threats.
Connecting inventory sources, tracking remediation, and building repeatable workflows across enterprise systems.