SECURITY OPERATIONS / TELEMETRY OPTIMIZATION
Logging Reduction Initiative
Windows Audit Policy Investigation & Validation
- Professional work, summarized
- Windows Event 4703
- Controlled device testing
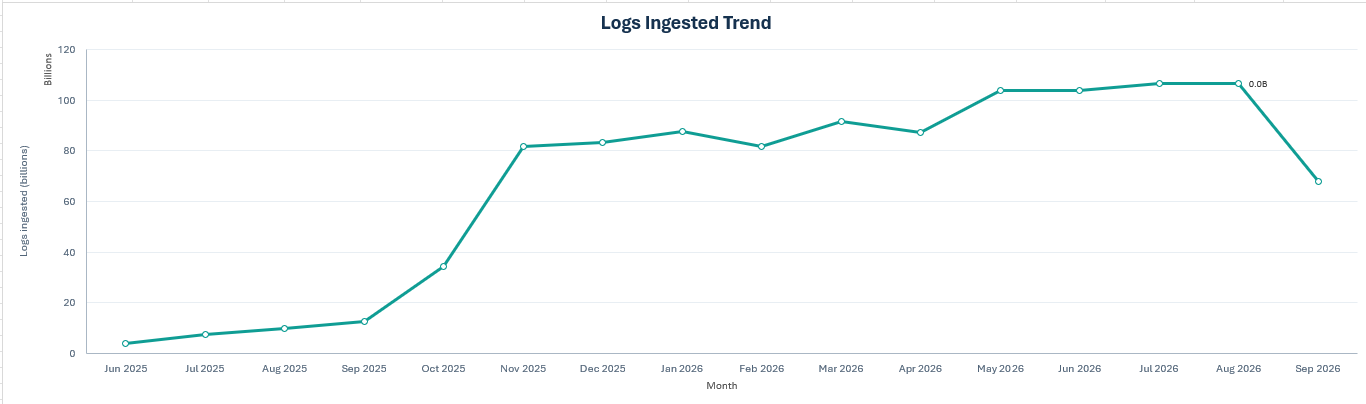
Contributed to a logging reduction initiative by investigating high-volume Windows Event 4703 activity, testing audit-policy changes, and validating ingestion behavior. Overall monthly log volume decreased approximately 36%, from 107 billion in August to 68 billion in September.
01 / RECORDED VOLUME
A visible drop, with context.
Lower monthly log volume
Recorded log volume fell from approximately 107 billion in August to 68 billion in September 2026 — about 36% lower month over month, comparing two complete months. These aggregate totals do not isolate the impact of the audit-policy change.
02 / INVESTIGATION
Trace the event to its policy.
I checked the current audit configuration and confirmed Event 4703 was reaching the SIEM. Before testing changes, I backed up the audit policy to retain a recovery reference.
I tested several candidate subcategories, documented their timing, and reverted the Authorization Policy Change test when it did not resolve the behavior. The successful configuration check showed Token Right Adjusted Events set to No Auditing.
This work required checking the observed event behavior rather than assuming that a similarly named audit category controlled it.
03 / VALIDATION
Test both directions.
- Observe the change. Event 4703 ingestion appeared to stop after the audit-policy change.
- Re-enable auditing. Events returned immediately in the test, giving me a way to check the relationship between the setting and the telemetry.
- Repeat the disable test. Ingestion stopped after approximately four minutes. I recorded the delay rather than assuming a policy change would be immediately visible in the SIEM.
04 / SECURITY JUDGMENT
Less telemetry is a tradeoff.
Disabling an audit subcategory removes its telemetry; lower volume alone does not establish better detection. My contribution was investigating the source, retaining a policy backup, testing reversibility, and documenting the observed response.
A broader rollout would need a review of detection dependencies, required audit coverage, the final policy baseline, and comparable before-and-after measurement windows.
Microsoft: Audit Token Right Adjusted Events ↗Scope & confidentiality
Sanitized account of my troubleshooting work. Internal device names, deployment details, raw logs, and device-configuration screenshots are omitted. The original aggregate ingestion graph is included above. The available evidence covers the observed test and aggregate chart; it does not establish fleet-wide deployment, restoration of every other tested subcategory, or unchanged detection coverage.